CoWIN leak: Indian govt refutes Covid vaccine portal data breach reports, orders probe


CoWIN
The Indian government refuted media reports of a major data breach in the Covid vaccination portal CoWIN. Issuing a statement, the Union Health Ministry said, "These reports allege a breach of data from the Co-WIN portal of the Union Health Ministry, which is the repository of all data of beneficiaries who have been vaccinated against Covid."
“Certain posts on the social media platform Twitter have claimed using a Telegram (online messenger application) BOT, the personal data of individuals who have been vaccinated is being accessed. It is reported that the BOT has been able to pull individual data by simply passing the mobile number or Aadhaar number of a beneficiary,” the statement said.
The ministry asserted that such reports are without any basis and are mischievous.
“Co-WIN portal of the Health Ministry is completely safe with adequate safeguards for data privacy. Furthermore, security measures are in place on the Co-WIN portal, with Web Application Firewall, Anti-DDoS, SSL/TLS, regular vulnerability assessment, Identity & Access Management etc. Only OTP authentication-based access of data is provided,” the statement further said.
The ministry also said that without a One-Time-Password (OTP), vaccinated beneficiaries’ data cannot be shared with any BOT.
The health ministry also requested the Indian Computer Emergency Response Team (CERT-In) to look into this issue and submit a report. In addition, an internal exercise has been initiated to review the existing security measures of CoWIN.
Pentagon revives mandatory testosterone testing for male troops aged 30 and above
FACT CHECK: Why did PM Modi ask Xi ‘is it okay’ at BRICS Summit? New video reveals...
India seeks to build a full semiconductor supply chain
From Abhishek Sharma to Sahil Chauhan, 5 batters with fastest T20I hundreds
Pyongyang dismisses US, western pressure over nuclear programme
US And Denmark reach Greenland deal, Trump announces expanded military presence
Google’s Gemini AI hacks real systems by guessing passwords during security test
US hiding troop deaths in Iran war? Toll higher than Pentagon count, claims report
China may have gained access to US's classified F-35 jets; parts meant for repairs diverted to Hong Kong, sparking Pentagon inquiry
NASA research plane reaches 61,000 feet over Panama
Godfather of AI Geoffrey Hinton gives US lawmakers a one-year warning on AI
Trump signs Russia sanctions law: India faces fresh 100% tariff threat over Russian oil
Brigitte Bardot’s private collection set for Paris auction; key items and prices revealed
Why Ranveer Singh’s Dhurandhar missed India’s Oscar entry; FFI jury member reveals what happened
Zendaya and Tom Holland step out for a low-key date in Los Angeles
‘Will go to any extent’: Pakistan vows to defend Saudi Arabia amid Houthi attacks
The Verdict | When precision fails: US commits war crime in Minab school strike, UN finds
Trump signs Russia sanctions bill into law, targets Moscow’s energy sector
66 years of the Indus Waters Treaty: How India and Pakistan settled a bitter river dispute
New Friday OTT releases (September 18, 2026): Lust Stories 3, You+Me, Best of the Best- 8 new titles coming on Netflix, Prime Video and more
Pak: A series of counter terrorism operations in Khyber Pakhtunkhwa
Fast bowler Brydon Carse faces no charges over Derby nightclub incident
Flying cars in UAE: Ras Al Khaimah signs deal with Chinese company to test new transport
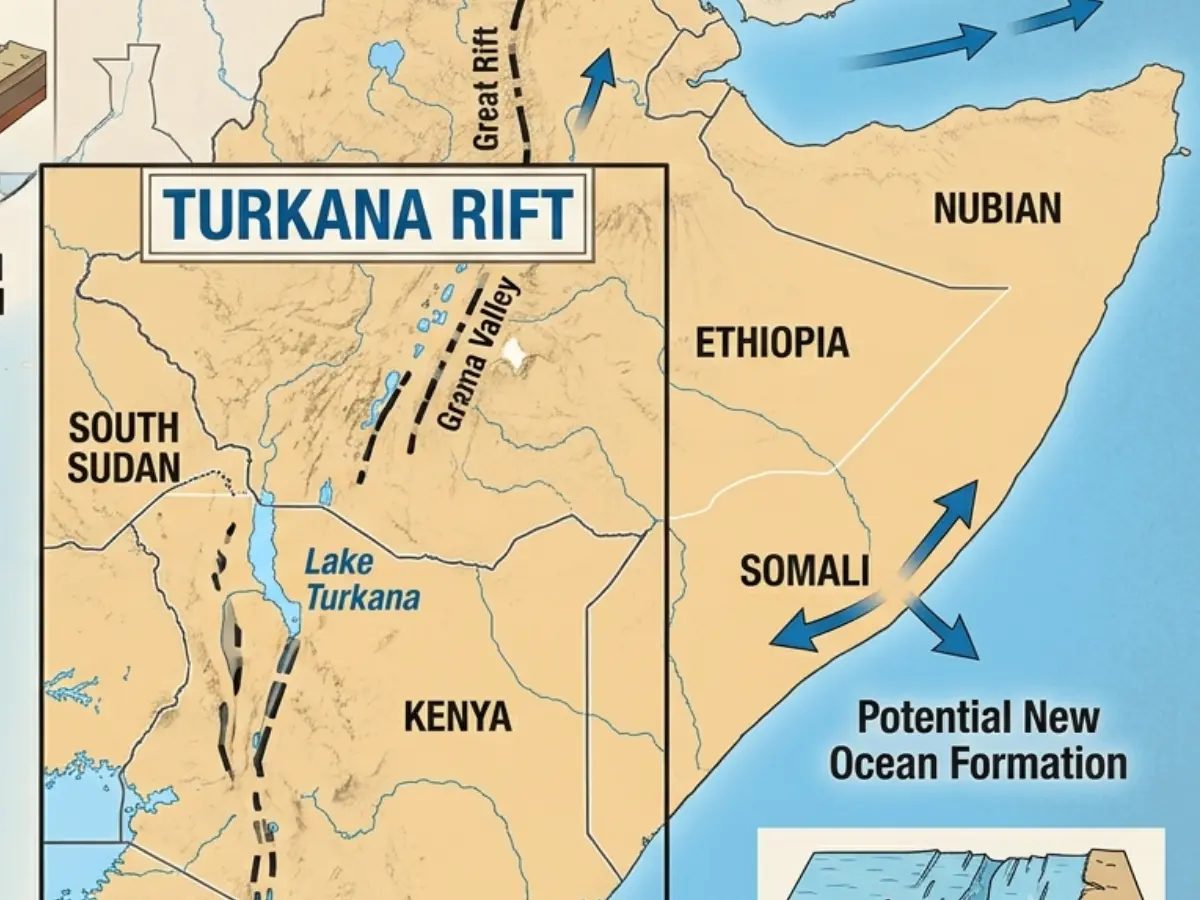
Africa is splitting, and a lot sooner than estimated, giving way to a new ocean
Trump bans CNN, MS NOW and Politico from White House over ‘FAKE NEWS’
Trump 2.0: Dark days ahead for America’s ‘imperial presidency’
Trump's Greenland dream comes true? POTUS announces 'Infinite Life' deal with Denmark, claims permanent US control
Tirupati Laddu ghee adulterated with chemicals, says ED, supplier arrested
Who is Khalilur Rahman? All you need to know about 81st UN General Assembly President
IIT Bombay student dies by suicide, was caught seeking AI help during exams
Meet top 5 bowlers in latest ICC T20I rankings
Indian Cinema bets big on mythology, brings ancient stories to modern audiences
Ukraine plans record $109 bn defence spending, nearly two thirds of budget amid Russia war
Russia holds first parliamentary elections since the beginning of the Ukraine war
Meet top 5 Indian batters with fastest T20I centuries
CERT-In in its initial report has pointed out that the backend database for the Telegram bot was not directly accessing the APIs of the CoWIN database.
What did the reports say?
Earlier on Monday, a section of the Indian media reportedthat the personal details of those registered to CoWINwere available on the messaging platform Telegram. According to a report by The News Minute, a Telegram bot hadbeen giving away the details of people who registered for vaccination including their names, date of birth, phone numbers, and other details provided at the time of registration, such as passport or Aadhar numbers among others.
As per a report by Kerala-based Malayala Manorama, if the mobile number of a person was entered, the above details were provided as a reply in an instant by Telegram. The details could be accessed even if the Aadhar number was entered instead of the mobile number, the report added.
Passport numbers of people who updated CoWINfor travelling abroad were leaked. The Manorama report also said that sincemany members of a family registered themselves on the portal under a single phone number, their details were also available on Telegram.
TMC’s Saket Gokhale alleges data breach of politicians, journalists
The data breach also leaked the details of many prominent politicians and journalists in India. In a Twitter thread, Trinamool Congress (TMC) leader Saket Gokhale shared screenshots of the details of politicians and journalists being leaked.
"There has been a MAJOR data breach of Modi Govt where personal details of ALL vaccinated Indians including their mobile nos., Aadhaar numbers, Passport numbers, Voter ID, Details of family members etc. have been leaked & are freely available," Gokhale tweeted and slammed the central government of not being aware of the leak and not informing citizens about the same.
"Who has the Modi Govt given access to sensitive personal data of Indians incl Aadhaar & Passport nos. which enabled this leak?" the TMC leader added and called the breach "a matter of serious national concern."
WATCH WION LIVE HERE
You can now write for wionews.com and be a part of the community. Share your stories and opinions with us here.