SBI confirms data breach: 3,897 records flagged on dark web. Is your money safe?


File: State Bank of India (SBI) Chairman Challa Sreenivasulu Setty (or C.S. Setty) addresses a press conference on the Q1 FY27 financial results of the SBI, Aug 07, 2026. Photograph: (ANI)
SBI confirms customer data may be exposed on the dark web, with 3,897 records flagged. Is your money and banking safe? All you need to know.
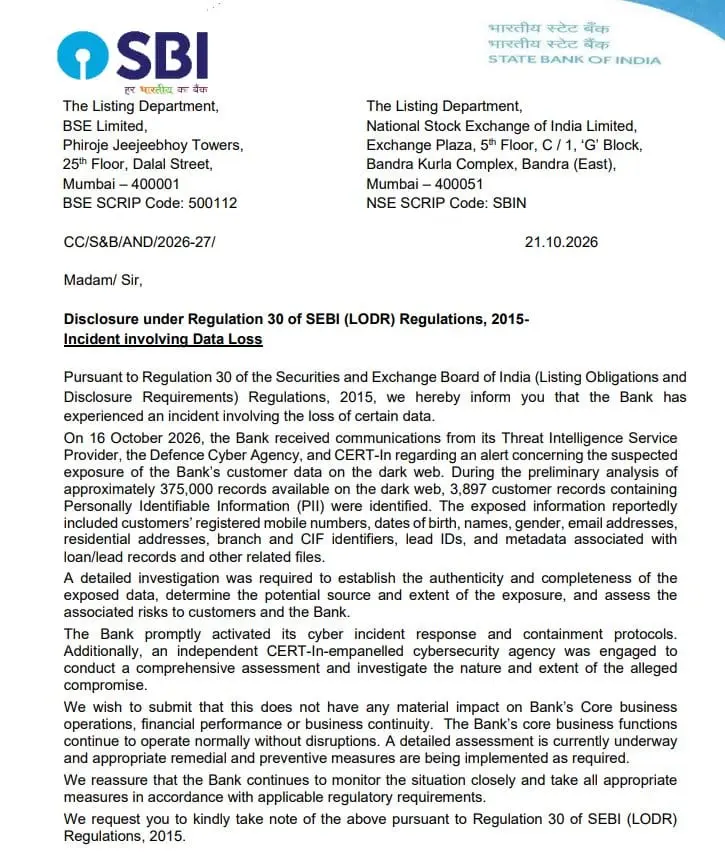
State Bank of India on Wednesday (Oct 21) confirmed that customer information may have been exposed online. In a formal disclosure, the bank said its Threat Intelligence Service Provider, the Defence Cyber Agency, and CERT-In alerted it on 16 October about data suspected to be linked to SBI customers appearing on the dark web. An initial review of roughly 375,000 records found online flagged 3,897 that contained personally identifiable information. The details, as per the bank, include Personally Identifiable Information (PII) like mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch and CIF identifiers, lead IDs, and metadata tied to loan and lead records.
This comes as a hacker group which calls itself ‘Siriusim’ claimed to have gained access to 3.8 lakh data entries, including customer personal data.
Also read | IMF World Economic Outlook: 10 economies to watch for growth in FY27 and FY28 - Where does India stand?
What this means for your money
The bank, which is India's largest lender, said customers' money and banking services are safe but urged caution against phishing. It said that accounts, funds and transactions continue to work as normal. According to SBI, this is a data exposure, not a compromise of account access or money.
Trending Stories


“We wish to submit that this does not have any material impact on Bank's Core business operations, financial performance or business continuity. The Bank's core business functions continue to operate normally without disruptions.”
The bank says it has switched on its cyber incident response and containment protocols. "Additionally, an independent CERT-in-empanelled cybersecurity agency was engaged to conduct a comprehensive assessment and investigate the nature and extent of the alleged compromise," it said. A detailed assessment is underway, along with remedial and preventive steps, the bank added.
Hacker group claims access to 3.8 lakh data entries
Previously, an unidentified group calling itself "Siriusim" claimed to have gained access to around 3.8 lakh data entries and 2,722 PDF documents linked to SBI. The claim was flagged by the cybersecurity monitoring account CyberPulse56 on 16 October. CyberPulse56 has cautioned that if the dataset is genuine, it could be used for identity theft, financial fraud, targeted phishing and fraudulent loan applications.
How customers can protect themselves
While the probe continues, a few habits can keep you safe:
- Never share OTPs, passwords or card details with anyone who calls, texts or emails you. SBI will never ask for these.
- Avoid clicking links in messages that claim to be from SBI and ask you to "verify" or "update" details.
- Keep an eye on your account statements and transaction alerts.
- Report anything suspicious to your bank at the branch or via the official helpline.

